Products / Compact
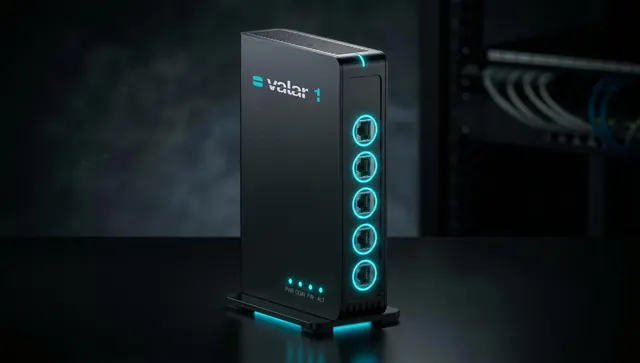
Valar 1 is the entry model of the family. It sits on a desk or in a network cabinet and has the same protection features as the larger models. Several sites can be managed centrally with one set of rules.
Overview
Valar 1 at a glance.
In small companies, nobody usually looks after IT full-time. Valar 1 is therefore designed to be low-maintenance: the interface is clear, neonotu provides the updates, and a service provider can look after the appliance remotely.
The network ports are on the side of the housing. Internet access, office network, telephony and guest Wi-Fi can be connected separately, each protected by its own rules.
Key facts
| Suited for | Medical practices, law firms, branch offices and small offices |
|---|---|
| Users | up to approx. 25 users |
| Inspection throughput | up to 1 Gbit/s |
| Form factor | Desktop unit |
Preliminary figures from the pilot program. Binding data sheets are available on request.
Use cases
Typical use.
- 01
Medical practice or group practice
Practice management, medical devices and guest Wi-Fi run in separate areas. Several sites are connected via VPN.
- 02
Law firm, tax office, agency
Confidential client data stays in the internal network. Staff working from home use VPN as if they were in the office.
- 03
Branch office with VPN to headquarters
The branch is permanently connected to headquarters over an encrypted link. Rules are maintained centrally and apply everywhere.
Data sheet
Valar 1 Technical data.
| Class | Compact |
|---|---|
| Suited for | Medical practices, law firms, branch offices and small offices |
| Users | up to approx. 25 users |
| Inspection throughput | up to 1 Gbit/s |
| Form factor | Desktop unit |
|---|---|
| High availability | – |
| Ports, dimensions, power consumption | in the full data sheet, on request |
| Firewall | stateful, rules by network, service, user |
|---|---|
| NAT | port forwarding, 1:1, outbound |
| Networks | VLAN (802.1Q), IPv4 and IPv6 |
| Country rules | GeoIP, address groups |
| Multiple internet lines | load balancing and failover |
| Prioritisation | traffic shaping (QoS) |
| Site-to-site | IPsec |
|---|---|
| Mobile staff | WireGuard, OpenVPN |
| Authentication | certificate, user account, one-time password (2FA) |
| Intrusion prevention | inline IPS, rule sets with automatic updates |
|---|---|
| SSL inspection | configurable per zone |
| Web filter | categories and block lists, including transparent mode |
| Behaviour detection | NeoI |
| Guest access | captive portal with vouchers |
| Interface | web interface, API |
|---|---|
| Multiple appliances | central management |
| Users | Active Directory, LDAP, RADIUS |
| Analysis | reports, NetFlow, packet capture |
| Configuration | change history with rollback, encrypted backup |
| Network services | DHCP, DNS (including encrypted), dynamic DNS |
| Scope | all features included, no add-on modules |
|---|---|
| Term | as agreed |
| During the term | updates, security updates, detection data |
Preliminary figures from the pilot program. Binding data sheets are available on request.
neonotu GmbH · Edelsbergstraße 8 · 80686 Munich, Germany · +49 89 2000 79 750 · mail@valarsecure.com · www.valarsecure.com
Included
The same features as every Valar.
Zone-based firewall
Rules by network segment, application and user. Office, production, guests and servers stay separate.
Intrusion prevention (IPS)
Known attacks are detected in network traffic and blocked before they reach systems on the network.
SSL inspection
Encrypted traffic can be inspected. For each zone you decide where this makes sense and where it does not.
VPN
Sites and mobile staff are connected over encrypted links, for example via IPsec.
Web filter
Access to malicious or unwanted websites is blocked by category.
NeoI
neonotu’s own AI detects unusual behaviour even where no signature exists yet.
Operations
Easy to run.
Central management
Several units and sites are managed in one place. Rules apply consistently, deviations stand out.
High availability
From Valar 2 upwards, two units work as a pair. If one fails, the other takes over. Valar 4 can be extended into a cluster.
One licence
The licence depends on the model and the term. There are no features that have to be bought separately later.
Questions
Frequently asked questions.
Is Valar 1 enough for our office?
For up to about 25 users, yes. What matters more than the number of people is the traffic: if you work a lot with large files or video calls, or want to inspect all traffic with SSL inspection, take a look at Valar 2. We are happy to advise you.
Is Valar 1 available as a high-availability pair?
No, pair operation starts with Valar 2. For small sites, one appliance is usually enough. In case of a defect, we repair or replace it.
What is included in the licence?
All protection features: firewall, intrusion prevention, SSL inspection, VPN, web filter and NeoI. The licence depends only on the model and the term; there are no add-on modules.
What happens when we grow?
You move to the next model. Because all models run the same software, rules and settings are carried over.
Who sets up the appliance?
Your IT service provider or one of our partners. On request, neonotu can also run the firewall for you as a managed service.
Is this the right model for your network?
Tell us briefly how many users and sites you have. We will recommend the right model and prepare a quote.
Ask for advice